Course: Software Security (KOSEN69) · Covers: Weeks 1–6 Time: 150 min · Total: 100 pts · Individual · Sandbox targets only (ethics policy applies).
Name: ____________________ Student ID: ____________
Each challenge yields a flag in the form
FLAG{...}(or the proof noted). Submit, per challenge: the flag, the payload/command you used, and a one-line mitigation. Partial credit for documented progress without the flag.
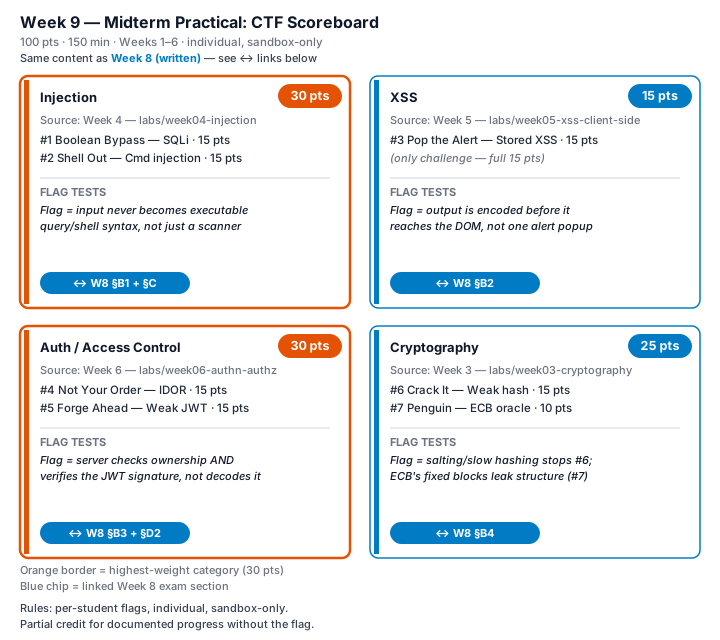
Targets — your flags come from your own instance in the hosted CTFd (account + WireGuard VPN setup: arena-vpn-guide (../../docs/arena-vpn-guide.md)):
- All 7 challenges: spawn your own instance of each in CTFd. The flag you submit must come from your instance.
- Running the lab folders locally (
docker compose up) is practice only: it serves public demo flags (FLAG{..._demo}), which are not a valid submission.
Challenges
| # | Title | Topic | Pts |
|---|---|---|---|
| 1 | Boolean Bypass — log in as admin without the password | SQLi (W4) | 15 |
| 2 | Shell Out — read a file via the host parameter | Command injection (W4) | 15 |
| 3 | Pop the Alert — fire alert(document.domain) stored for another user | Stored XSS (W5) | 15 |
| 4 | Not Your Order — read another user's order object | IDOR (W6) | 15 |
| 5 | Forge Ahead — become admin with a forged JWT | Broken JWT (W6) | 15 |
| 6 | Crack It — recover a password from a weak hash | Crypto (W3) | 15 |
| 7 | Penguin — recover the plaintext structure from the ECB oracle | Crypto (W3) | 10 |
Submission table (fill in):
| # | Flag / proof | Payload or command | Mitigation (1 line) |
|---|---|---|---|
| 1 | |||
| 2 | |||
| 3 | |||
| 4 | |||
| 5 | |||
| 6 | |||
| 7 |
Rules: no collaboration; attack only the provided targets; document your steps. Pairs with the Week 8 written midterm.