DevSecOps: Putting It Together
Software Security · Nutthakorn Chalaemwongwan
Today
- Security in the CI/CD pipeline
- Logging, monitoring & alerting
- Failing safely
- Vulnerability mgmt & disclosure
- 🎮 Game: Break the Build (Red vs Blue)
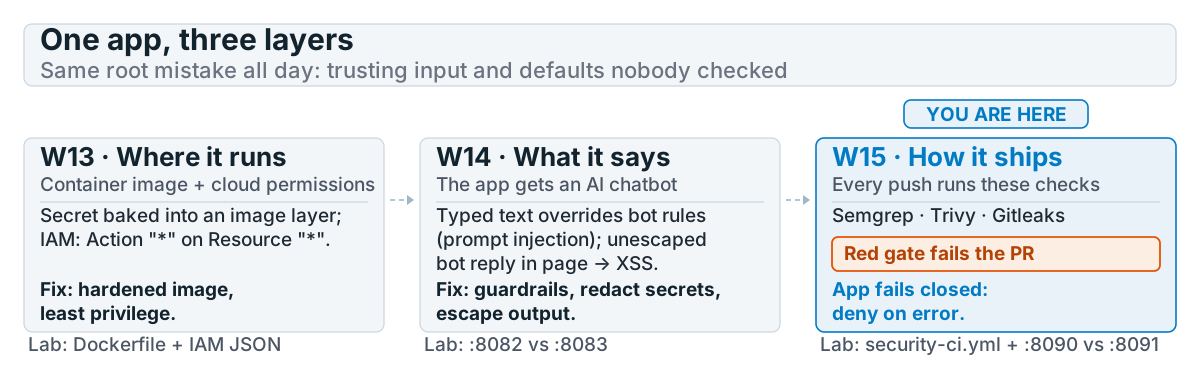
The whole course in one pipeline
- SAST (Wk2) · SCA + image scan (Wk12–13) · IaC (infrastructure-as-code) config scan (Wk13) · secret scanning (Wk2)
- Automated gates instead of one-off scans
- Secure by Design as the default
One push, three jobs
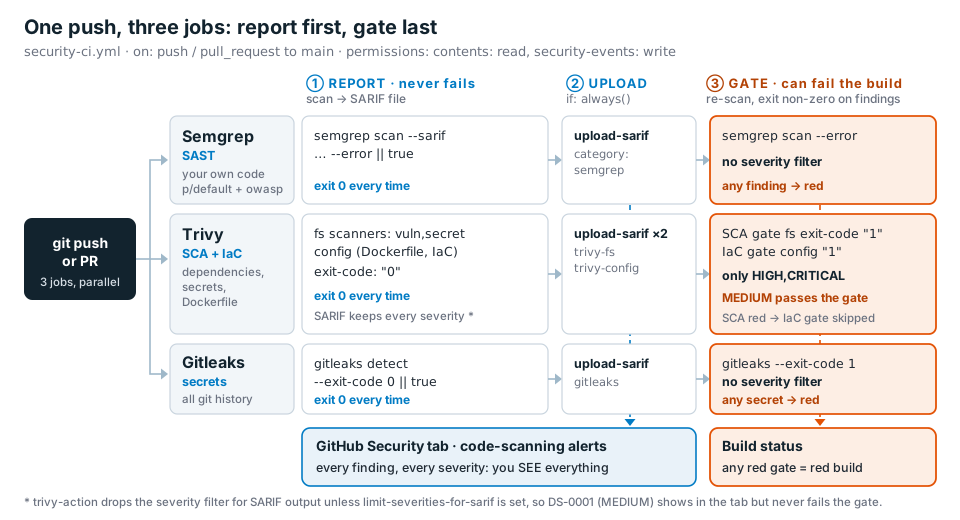
A security gate
# .github/workflows/security-ci.yml
- semgrep   # SAST
- trivy     # SCA (fs) + IaC (config) — image scan is optional, off by default
- gitleaks  # secrets + git history
# each tool runs TWICE: once to report (SARIF, always), once to gate (fails the build)- The token gets only what it needs:
contents: read,security-events: write - Results (SARIF) go to the GitHub Security tab
- A red run blocks a merge only if the jobs are required checks (branch protection)
Platform option — GitHub Advanced Security
- CodeQL code scanning (SAST) on every PR
- Secret scanning + push protection
- Dependabot for vulnerable deps
- SonarQube as a quality/SAST gate alongside
Same idea as the YAML gate — managed, in the repo.
Logging, monitoring, alerting
- A09:2025 — without logs you can't detect or respond
- Log security events (authn, authz failures, anomalies)
- Never log the secret/token value itself (CWE-532) — log
reason=bad_token, not the token - Alert on suspicious patterns
Detection tooling
- NIDS (network intrusion detection) — Snort / Suricata watch network traffic
- HIDS (host intrusion detection) — OSSEC watches one machine
- SIEM (collects and connects alerts) — Security Onion bundles these tools
- Network visibility: TAP (lossless) vs SPAN (cheap, can drop)
Alerts — the confusion matrix
| Incident real | No incident | |
|---|---|---|
| Alert fired | True positive ✅ | False positive |
| No alert | False negative 💀 | True negative |
- False negative = worst case (missed attack)
- Some false positives are inevitable — tune, don't silence
When something happens (NIST SP 800-86)
Collection → Examination → Analysis → Reporting
- Collect what disappears first (order of volatility): memory → temp files → disk → logs
- Failed/success logins: Windows Event 4625 / 4624
Fail safely
- A10:2025 — mishandled errors leak info / fail open
- Fail closed: deny on error, don't bypass checks
- Don't expose stack traces / secrets in errors
Vulnerability management & disclosure
- Triage by severity; track to remediation (SLAs)
- Coordinated disclosure & bug bounties
- security.txt; a path for researchers to report
One decision, made twice
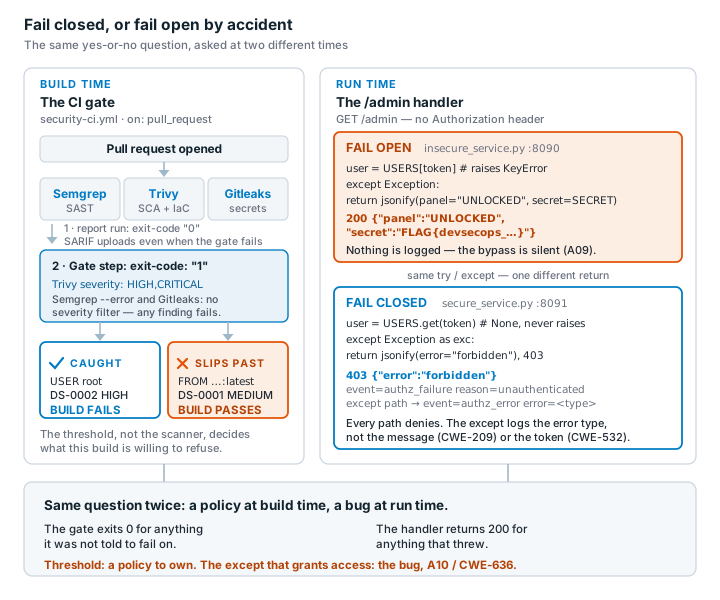
Try it — same request, two services
Pick a token. Both real services answer, and you see what each one logs.
🔴🔵 Game — Break the Build
- Blue: set up the gate (Semgrep + Trivy + Gitleaks), fail on HIGH/CRITICAL, log security events and deny on error
- Red: one planted defect per PR — an old dependency (Trivy SCA), a Dockerfile running as root (Trivy config), or a hard-coded token (Gitleaks)
- Score: Blue +1 per catch · Red +1 per defect that slips through (e.g.
chmod 777,FROM :lateststay green) — then propose a rule that would catch it - Flag: leak it from the fail-open
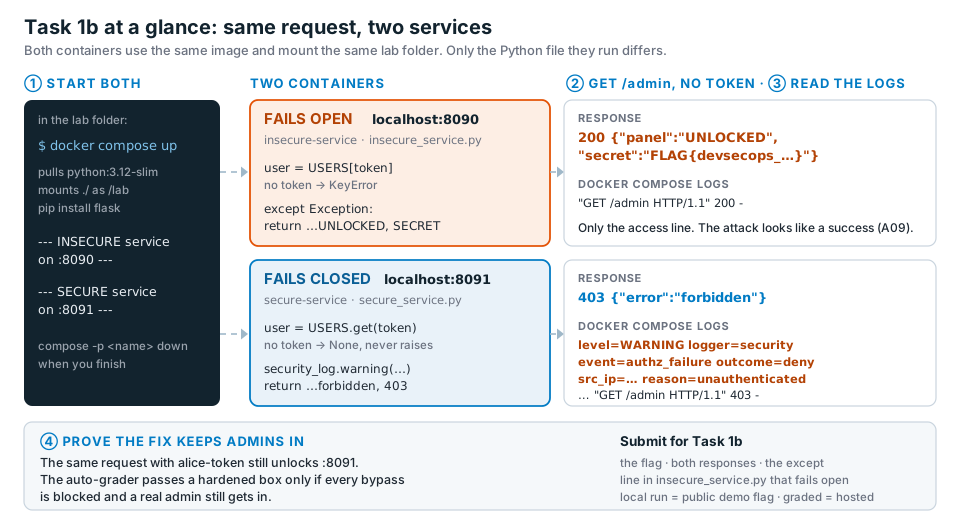
/adminininsecure_service.py(local run = demo flag; graded flag = your hosted instance)
Break the Build — what each change turns red
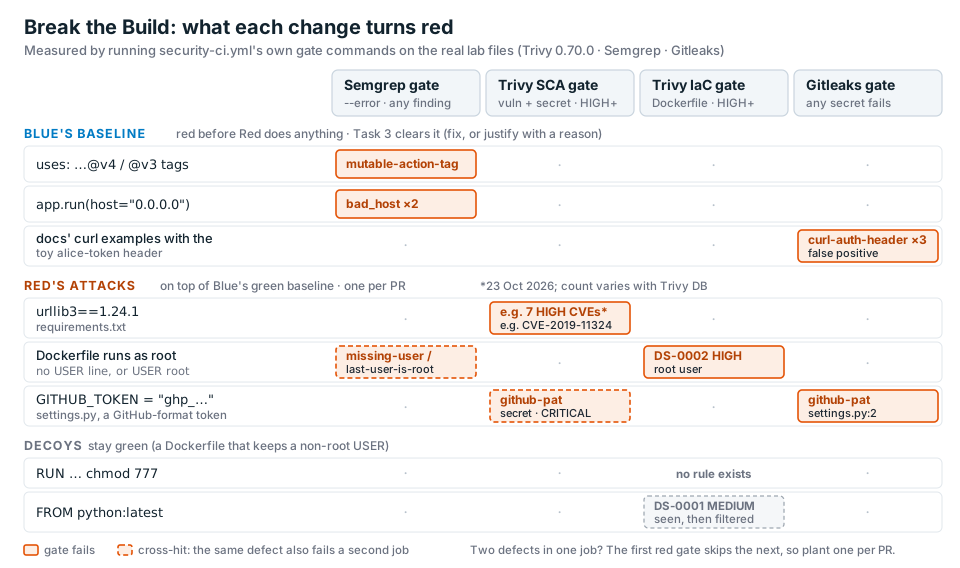
Try it — which job goes red?
Click Blue's clean baseline, then Red: old urllib3, and find the gate that fails.
Task 1b at a glance
Deliverable
📋 Worksheet 15 —
labs/week15-devsecops-pipeline/worksheet.md(Part 3) · start: pushsecurity-ci.ymlto your own public repo → GitHub Actions; for the flag,docker compose up→ :8090 (insecure) / :8091 (secure)
- A passing PR that adds the pipeline
- A screenshot of the failing gate step for your planted defect, and which job caught it
- The
FLAG{...}from the fail-open/admin, written in the worksheet (graded flag: your hosted instance) - + Audit the AI / EiPE / Prompt Problem (see worksheet)
Key takeaways
- Automate security gates — humans forget, pipelines don't
- You can't defend what you don't log
- Fail closed; disclose responsibly
Questions?
Next week: Capstone studio & CTF warm-up