
All weeks · Overview · CTF brief

Week 9 · Lecture slides

Week 9

Contents5 sections

Midterm — Hands-on CTF Practical

Covers Weeks 1–6 · Individual


Format

  • Timed, in the sandbox
  • Each solved challenge = a flag = points
  • Partial credit for documented progress

Challenge areas — 100 pts, 7 challenges
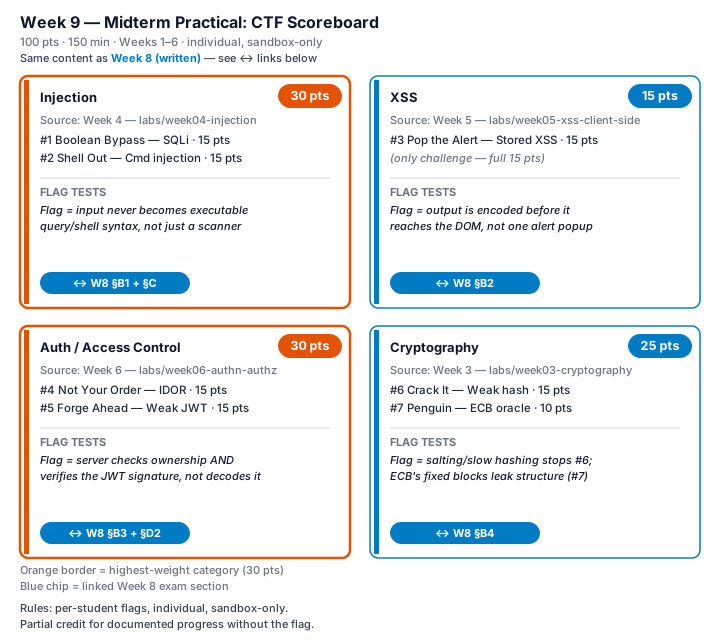
Four categories: Injection (30 pts) from Week 4 — Boolean Bypass SQLi and Shell Out command injection, 15 each. Auth and Access Control (30 pts) from Week 6 — Not Your Order IDOR and Forge Ahead JWT forgery, 15 each. Cryptography (25 pts) from Week 3 — Crack It password cracking (15) and Penguin ECB oracle (10). XSS (15 pts) from Week 5 — Pop the Alert, stored only. Not against DVWA or Juice Shop — this course's own apps, the only targets a flag is actually planted on.


Rules

  • Sandbox targets only — ethics policy applies
  • Submit 3 fields per challenge: flag/proof, payload/command, one-line mitigation
  • No collaboration

Submit your flags

Next: Week 10, API security

All weeks in Software Security